WellSpend · Cloud FinOps Your cloud bill, judged against the performance it buys.
- Read-only by design
- AWS
- Well-Architected
- Org-wide
A strictly read-only FinOps and Well-Architected review across every AWS account in your organisation. It surfaces up to 25% in savings with a prioritised roadmap — and never changes a thing.
- Up to 25%
- Typical savings surfaced across an AWS estate
- Zero write access
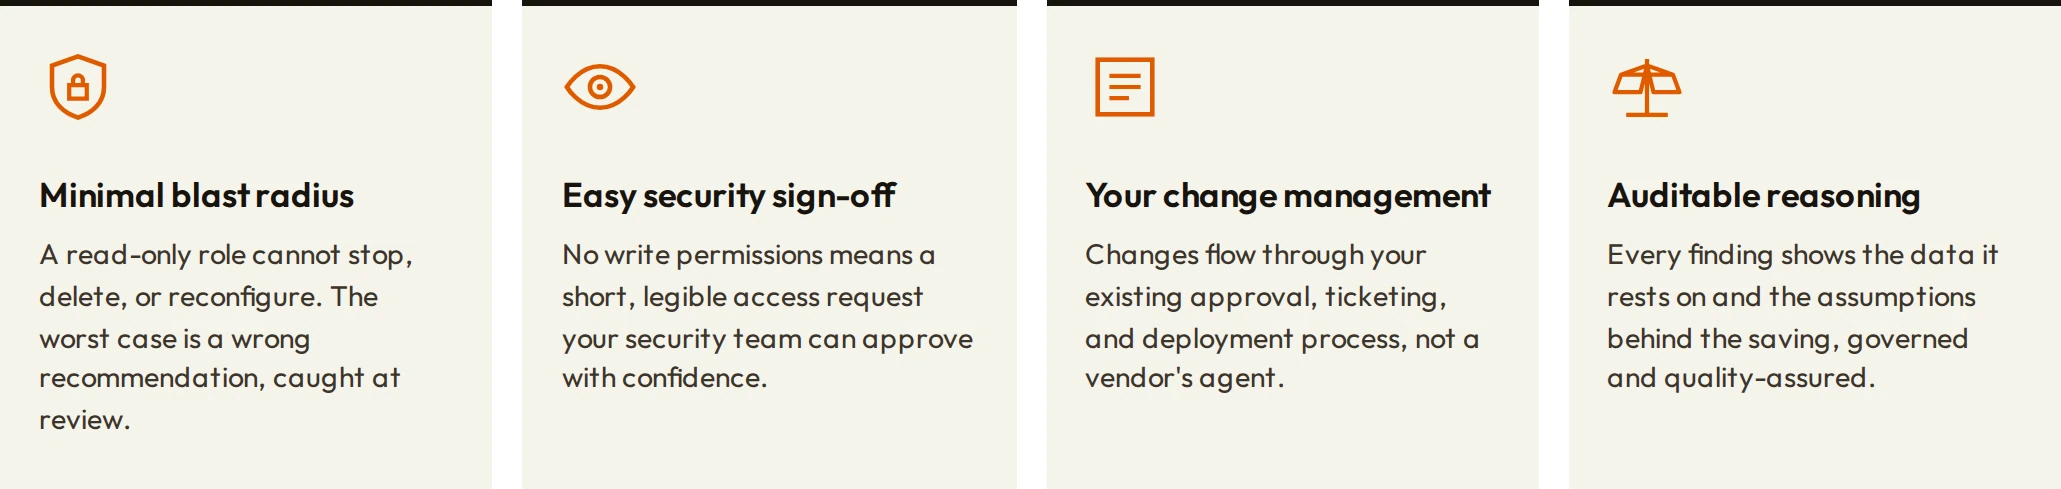
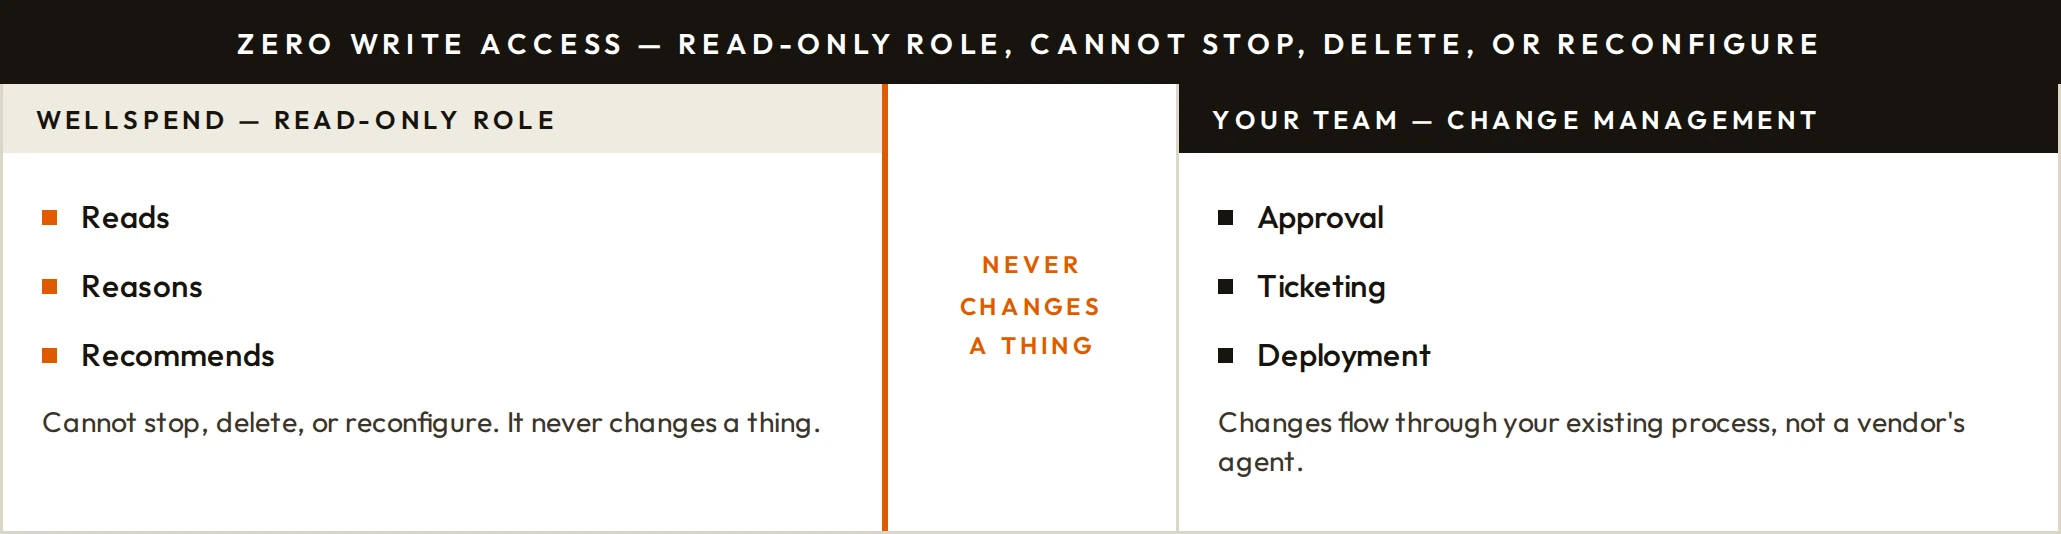
- Read-only role — cannot stop, delete or reconfigure
- Org-wide, one pass
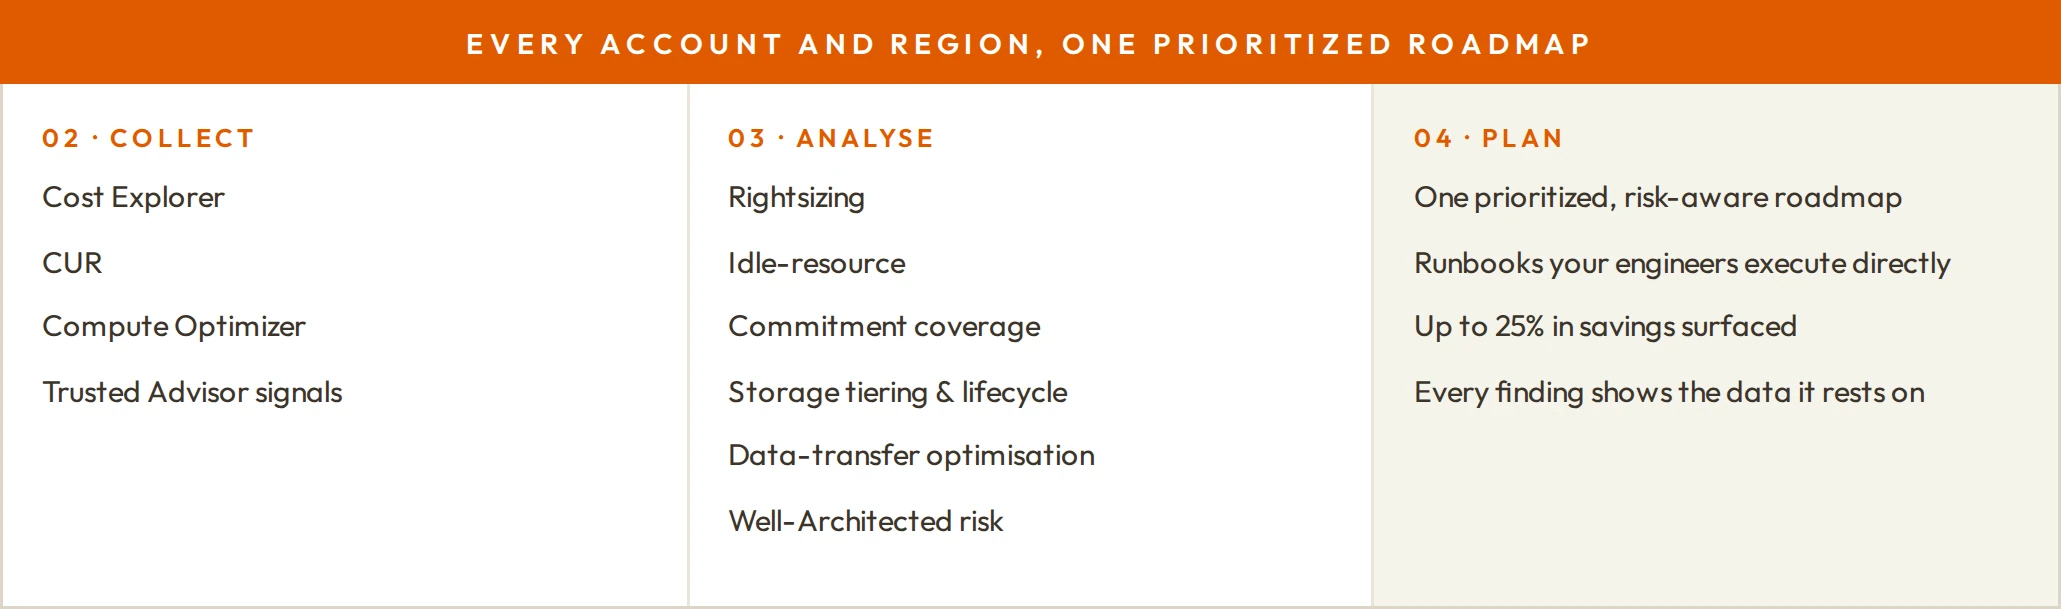
- Every account and region, one prioritised roadmap
Why WellSpend
Why “read-only by design” matters.
The risk
One broken production change
The fastest way to lose a FinOps engagement is to break production chasing a saving. Tools with write access ask your team to accept that risk before the value is proven.
The usual answer
A consultant snapshot
A point-in-time spreadsheet from a few sampled accounts. Accurate the week it lands, stale the month after, and rarely mapped to Well-Architected risk.
WellSpend
It never changes a thing
A read-only role across your whole organisation. Rightsizing, idle resources, commitment coverage, storage tiering and data transfer — quantified, prioritised and handed to your engineers to execute through your own change process.
How it works
How WellSpend runs.
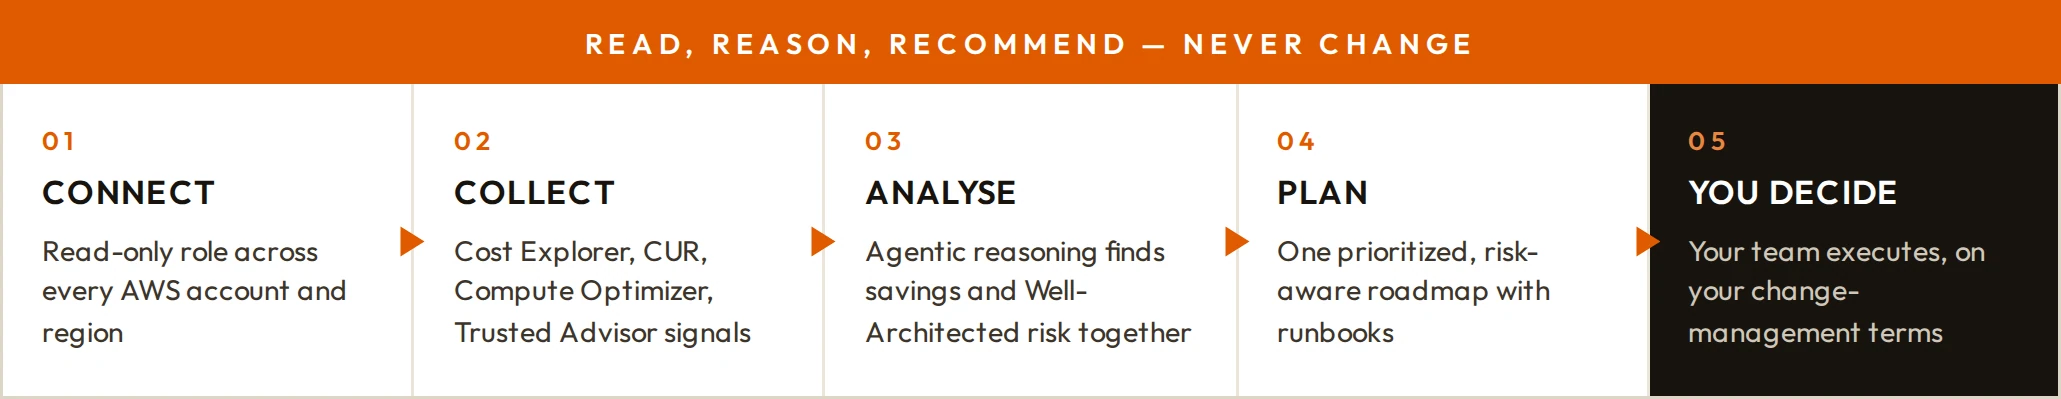
/ 01
Connect
A read-only role across every AWS account and region.
/ 02
Collect
Cost Explorer, CUR, Compute Optimizer and Trusted Advisor signals.
/ 03
Analyse
Agentic reasoning finds savings and Well-Architected risk together.
/ 04
Plan
One prioritised, risk-aware roadmap with runbooks.
/ 05
You decide
Your team executes, on your own change-management terms.
See it on your own data
Watch WellSpend work on a real use case, in a 30-minute live demo.
Free. Then a scoped proof of concept at no cost, before you commit.
Inside the solution
WellSpend, drawn out.
What you get
Outcomes you can hold us to.
Up to 25% in savings surfaced, with a prioritised roadmap
Strictly read-only — no write access, ever
Rightsizing, idle-resource and commitment-coverage analysis, quantified
Storage tiering, lifecycle and data-transfer optimisation
Well-Architected risk read beside the savings, not separately
Runbooks your engineers execute on your own change process
Built for
- CFOs & FinOps leaders
- Cloud & platform engineering
- CISOs & security teams
- Infrastructure & SRE leads
Industries
- All industries
Works with
- AWS
- Cost Explorer
- CUR
- Compute Optimizer
- Trusted Advisor
Free demo and no-cost proof of concept
Approve a read-only role on 2–3 accounts and see your number.
2–3 AWS accounts · read-only role · no cost
The scope
- You approve a read-only IAM role on 2–3 accounts
- We run the full FinOps and Well-Architected read across them
- Nothing in your estate is stopped, deleted or reconfigured
You provide
- A read-only IAM role on 2–3 representative accounts
- Cost and Usage Report (CUR) access, or Cost Explorer read access
- 30 minutes with someone who knows the workloads
You get
- A quantified savings number for those accounts
- A prioritised, risk-aware roadmap your engineers can execute
- A Well-Architected risk read alongside the savings
FAQ · Deployment, data and cost
What buyers ask before they commit.
Have a question that is not answered here?
01Can WellSpend break anything?
No. It holds a read-only role and has no write path — it cannot stop, delete, resize or reconfigure any resource. Execution stays entirely with your team, on your change process.
02How is it different from AWS Cost Explorer or Trusted Advisor?
Those give you data and generic checks. WellSpend reasons across the whole organisation — rightsizing, idle resources, commitment coverage, storage and transfer — and returns a prioritised roadmap with the Well-Architected risk read beside each saving.
03Do you guarantee 25% savings?
No, and we say so plainly. Savings depend on your estate. Up to 25% is what we typically surface; the proof of concept (PoC) tells you your actual number before you commit to anything.
04Will it re-architect our applications?
No. Deep redesign is a separate engagement. WellSpend gives you the savings, the risks and the runbooks — it does not pretend to rebuild your applications.
05Where does it run?
It reads your AWS estate through a read-only IAM role you create and can revoke at any time. Nothing is installed in your accounts.
06What can it change without us?
Nothing at all. There is no write path. It cannot stop, delete, resize or reconfigure any resource — execution stays with your engineers, on your change process.
07Is our data used to train models?
No. Billing and configuration data produces your review and nothing else.
08What does it cost after the review?
The first review, on two or three accounts, is free. Production is priced against the estate under review — scoped on the call.
More solutions
10+ agentic solutions. One standard.
Spend & Sourcing Analytics
Agentic Sourcing Foundation
One governed spend foundation on your SAP data, with specialised AI agents for sourcing, contracts, finance and demand.
Explore
Performance Marketing
ApexAIQ
35 agents across seven crews work your Google and Meta accounts in parallel, 24/7.
Explore
Data Privacy & Compliance
DPDP-AID
DPDP Act compliance through true discovery — code, schemas and legacy data parsed for real lineage.
ExploreNext step
See your number, at no cost.
Book a free demo of WellSpend, or scope a no-cost proof of concept (PoC) on your own data. A senior engineer replies within one business day.